
In recent years, Telegram has become one of the main platforms used by cybercriminals for the distribution of stolen credentials. Thanks to easy access, guaranteed anonymity, and the ability to share files quickly, numerous Telegram groups and channels have become true marketplaces for the trade of compromised data.
Monitoring these channels is essential for those working in cybersecurity and threat intelligence. The information shared can help companies and professionals identify exposed credentials, prevent targeted attacks, and strengthen their defense strategies.
In this article, we highlight five Telegram channels that, in our view, every security analyst should keep an eye on to proactively detect any credential theft.
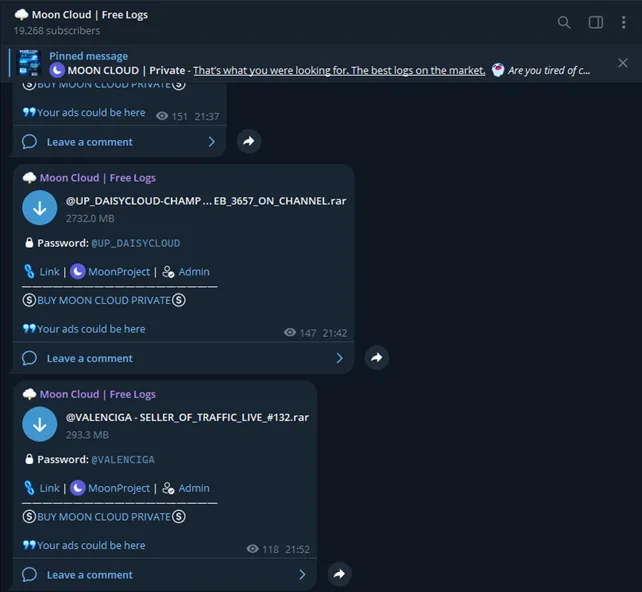
1. Moon Cloud | Free Logs
One of the most active channels in the credential leak landscape. Moon Cloud provides constant updates on breached databases, credential dumps, and new data leaks. Logs are published on a daily basis.
2. SNATCH LOGS CLOUD
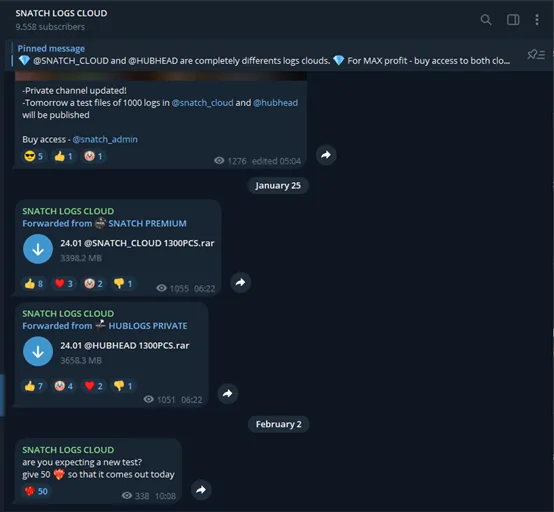
A channel focused on publishing credentials leaked from various online services. The admins constantly monitor dark web forums and marketplaces, reposting databases of compromised accounts in real time.
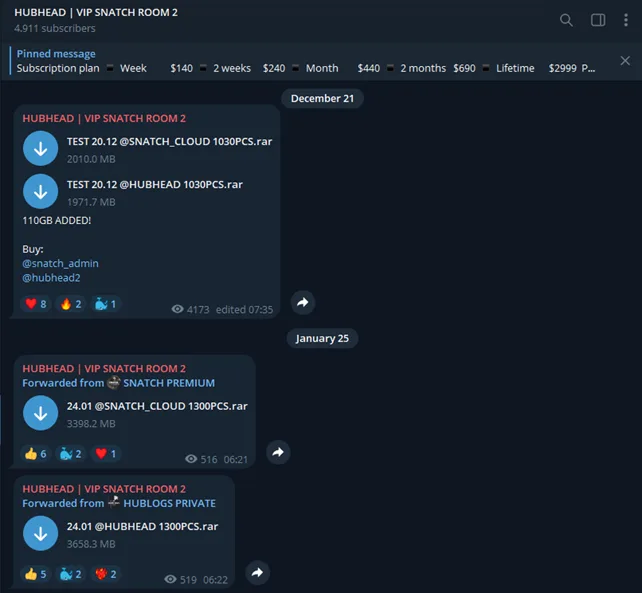
3. HUBHEAD | VIP SNATCH ROOM 2
This channel is similar to the previous ones, a bit less well-known and with less frequent posts. Still, it's a solid source for exfiltrated credentials.
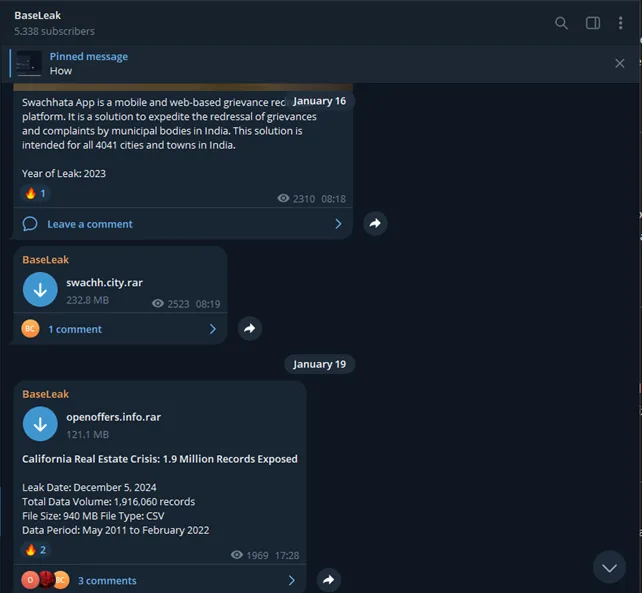
4. BaseLeak
Wrapping up our collection of the most active redistributors of compromised credentials in recent months. It has a lower posting frequency, but it's still worth monitoring.
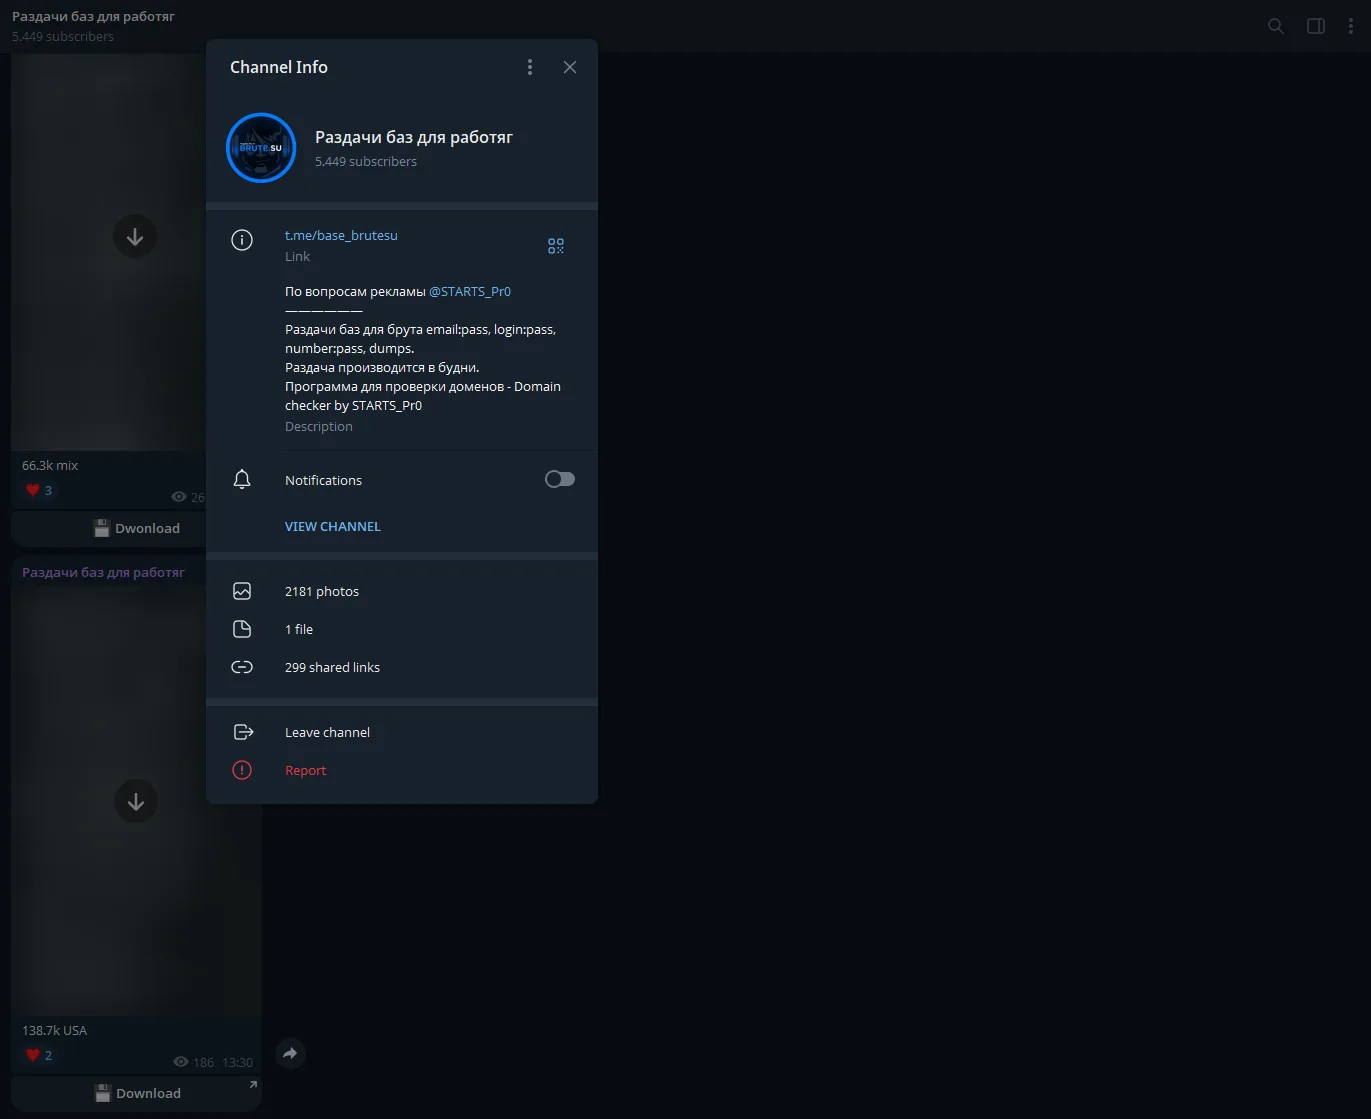
5. Base Brutesu (Раздачи баз для работяг)
A Russian-based Telegram channel, very active in recent months and which shares numerous collections of exfiltrated credentials.
Conclusion
Following these Telegram channels is critical for anyone working in cybersecurity and threat intelligence. Being aware of exposed credentials allows for timely action to mitigate the risk of cyberattacks and protect both personal and corporate accounts.
Constant monitoring of leaks is a proactive strategy that enables the detection of vulnerabilities before they are exploited.
With the growing prevalence of credential stuffing and phishing, staying informed about new data leaks is a necessity for every cybersecurity professional.